Security Center
Security evidence has a scope
The deployed E4S Monitor records certificate validity and expiry context for registered HTTPS assets. Operators can review check history and configured notifications when a certificate approaches expiry or a website check changes state. A valid certificate does not prove that the application behind it is secure.
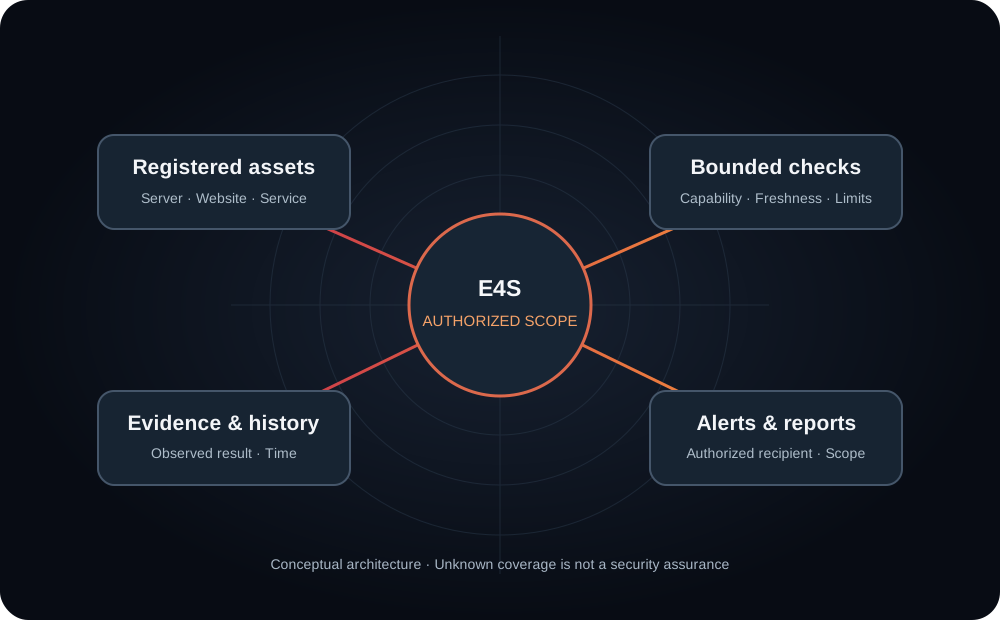
Illustrative workflow diagram, not a live scan result.
Current scanner availability
The separate Security Center vulnerability scanner and advisory feed are not enabled in this production Monitor. We do not claim vulnerability assessment of servers or websites from HTTP or TLS monitoring alone. For current coverage, review security scans and findings and use an approved assessment process for assets requiring deeper review.
Act on defensible evidence
Confirm the asset and timestamp, read the check evidence, and coordinate a certificate renewal or configuration change with the responsible operator. Never paste credentials or private keys into a support ticket.