SERVER MONITORING
Server health with context
Review CPU, memory, disk, load, network, service relationships, and agent freshness for registered Linux servers.
Explore serversMonitor registered assets, understand what changed, and act with a traceable record across your authorized workspaces.
Health, history, access, and action belong in the same operational context. E4S brings those pieces together for the assets and workspaces your team is authorized to manage.
Each capability below is described from the deployed E4S Monitor product. Availability depends on your configuration, role, and workspace.
Review CPU, memory, disk, load, network, service relationships, and agent freshness for registered Linux servers.
Explore serversFollow HTTP response behavior, redirects, certificate validity, expiry, and status history for authorized websites.
Explore websitesUse supported discovery, templates, policies, and manual checks to understand the services your infrastructure depends on.
Explore servicesConfigure email, Telegram, push, and sound channels where available; preferences and deduplication keep repeated events useful.
How alerting worksOperational reports and exports put the time range, affected assets, and supporting history beside the current condition.
Explore reportsReview certificate hostname, validity and expiry for registered HTTPS assets alongside check freshness.
SSL monitoringReview refreshed server, website, service and alert summaries with an explicit connection and last-update state.
Live Center guidePreserve operator context for an authorized server without treating notes as a store for secrets.
Notes guidanceRun authorized operations against selected assets with visible lifecycle, cancellation, and audit context.
Fleet operationsAuthenticated remote access follows workspace and role boundaries; commands are explicit and reconnect state stays visible.
Terminal guidanceWorkers, retries, leases and audit events give authorized infrastructure work a visible execution trail.
AutomationCertificate and operational security evidence is useful only when source, timestamp and coverage limits are clear.
Security coverageLive Center, notes, and reporting help teams connect a current condition to the evidence and follow-up around it.
Explore monitoring →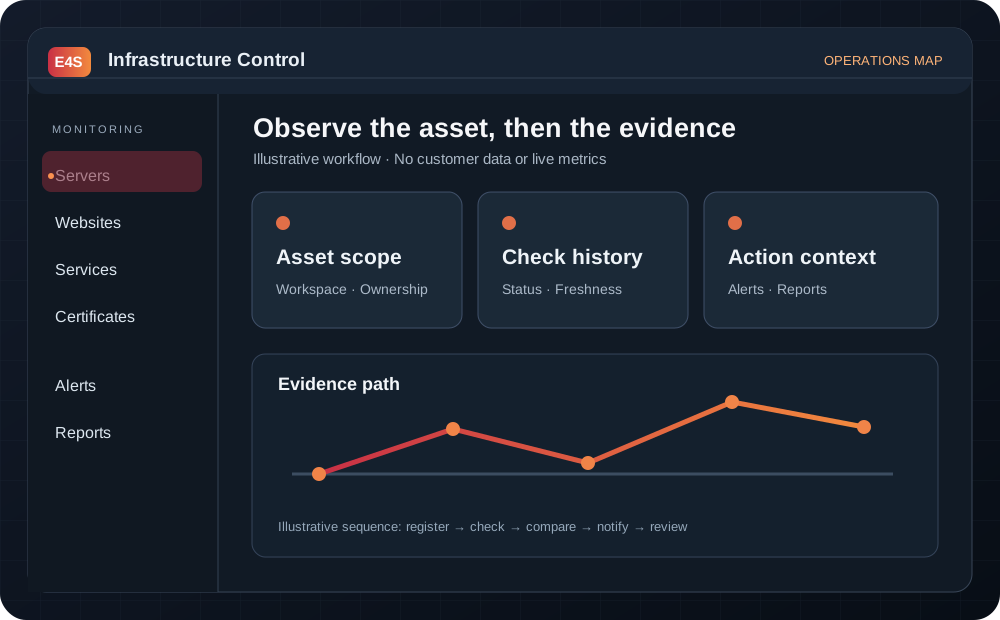 Illustrative product view; no live customer data
Remote work, security checks and reporting stay connected to workspace ownership and operator permissions.
Review access guidance →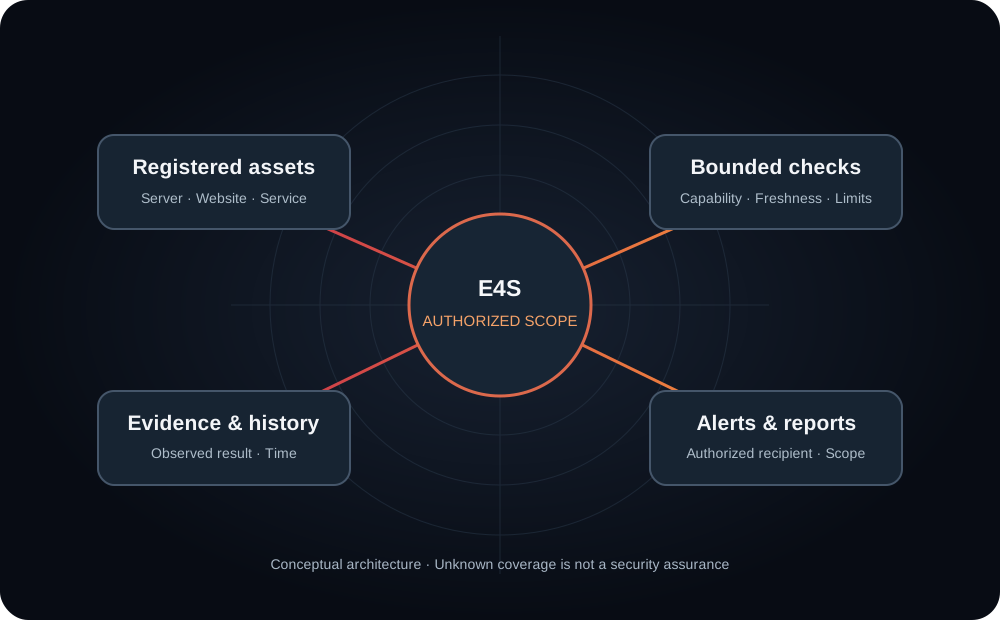 Illustrative product view; no live customer data
East4Serv works across Linux servers, Magento stacks, and private-cloud deployments. Monitoring provides evidence; an agreed management scope determines who makes changes and how they are reviewed.
Explore managed services →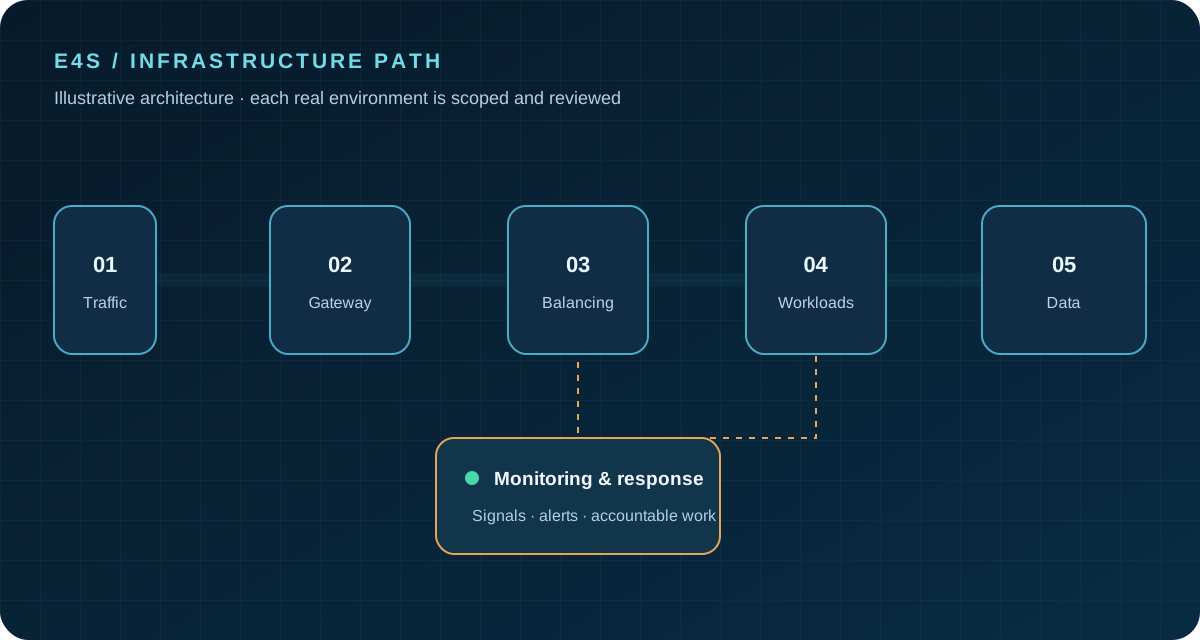 Illustrative product view; no live customer data
A scoped project records milestones, customer-visible tasks, target dates, and delivery updates. Customers can follow progress and respond from their portal without seeing private team notes.
Explore project services →Illustrative product view; no live customer dataEast4Serv’s public history begins with Linux and dedicated-server administration in 2007. Today its service catalog spans monitored infrastructure, managed operations, private cloud, and scoped engineering projects.
Compare the published asset capacities, then confirm current terms with East4Serv.
A smaller operating scope for teams beginning to centralize infrastructure monitoring.
29.00 USD / monthBroader asset and workspace capacity for teams managing more environments.
79.00 USD / monthExpanded capacity for infrastructure teams operating across many workspaces.
99.00 USD / monthGuides cover asset registration, monitoring evidence, alerts, reports, remote operations, and account boundaries.
Read the documentation →Review coverage and operating boundaries before connecting an asset.
The separate Security Center scanner is not enabled in the current production Monitor. Existing checks are limited to registered monitoring assets; do not use them as an arbitrary external scanning tool.
No. It is one piece of evidence. Security coverage depends on the scan mode, registered asset, agent capability, provider freshness, and checks that actually completed.
Yes, when your role and workspace permissions allow the scoped report download. Reports include coverage and limitation details.
The platform shows freshness and cached/grace state according to its configured contract. It does not silently claim current coverage or invent an all-clear result.
Tell us about your assets and operating model. We will help map the current E4S capabilities to the work your team needs to perform.
Contact East4Serv ↗